
Latest
The Attack Surface Has Moved to Vault Infrastructure
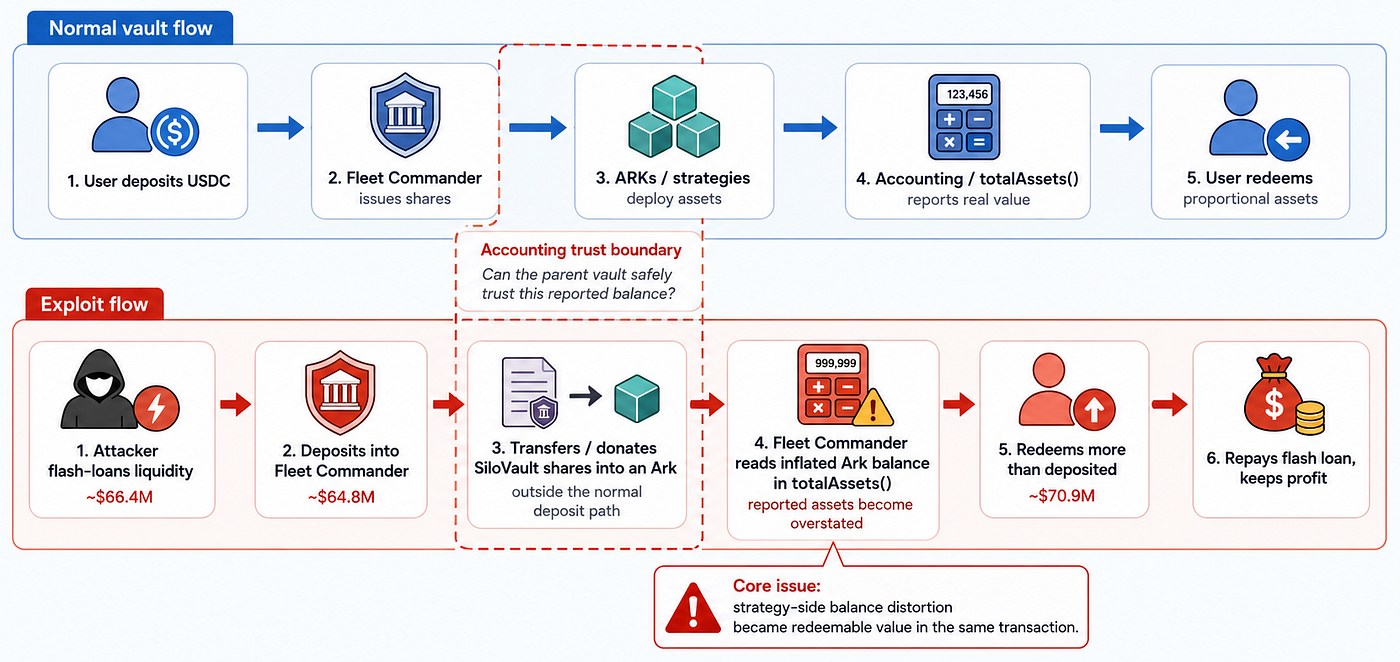
The $6 million Summer.fi exploit shows how vault accounting, stale asset values, strategy adapters, and operational controls define DeFi's attack surface.
Original analysis of onchain security, vault infrastructure, transaction policy, software supply chains, and AI agents—plus engineering notes from the systems we build.
Latest
The $6 million Summer.fi exploit shows how vault accounting, stale asset values, strategy adapters, and operational controls define DeFi's attack surface.
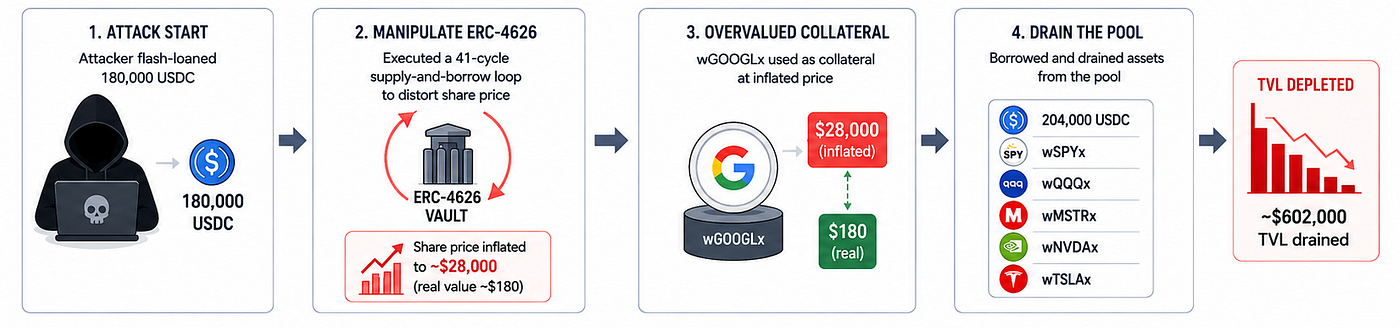
On July 1, 2026, Edel Finance, an Ethereum-based Aave-fork lending market, suffered an oracle manipulation exploit that caused an estimated loss of $403,000 according to Defimon Alerts.
April was one of the worst months crypto has seen for security losses. PeckShield reported 40 major hacks totaling about $647M in losses, the largest being Drift Protocol and KelpDAO.
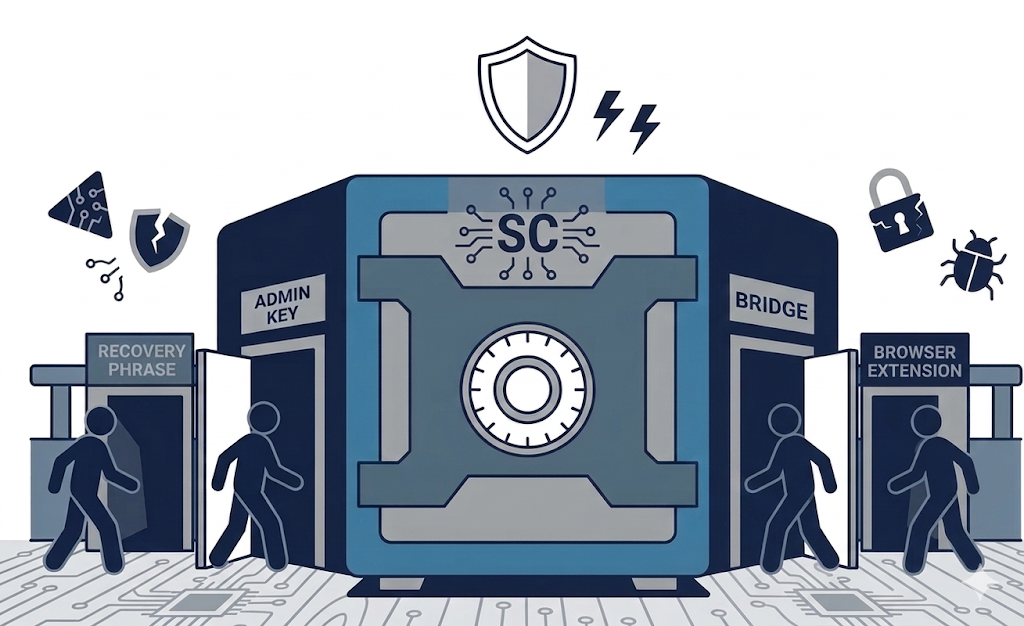
Early 2026 was not defined by one class of exploit. The total losses reported by security analysts varied widely because they counted different perimeters of risk.
A sourced review of 2025 crypto attacks, from software supply chains and protocol exploits to compromised signing infrastructure, with practical security lessons.
Christmas week has a predictable rhythm onchain: Fewer engineers awake, more retail activity, more “quick checks” on phones, more copying and pasting, more trust placed in familiar interfaces.
How a single biased nonce drained Upbit’s Solana hot wallet… and why the fix has been staring us in the face for years.
You pull in a familiar SDK on a Monday morning. The command scrolls by, a few extra lines from a preinstall script you don’t really read, and that’s it. No red flags. No flashing lights.
This post lays out how we think about incidents like Cloudflare’s outage this week, why pure smart‑contract control planes with timelocks change the failure modes, and where zero‑knowledge proofs fit.
Public forensics of the Balancer v2 incident point to a vault-level authorization or state-transition failure—and show why audited systems still need layered controls.
CISA's emergency F5 directive shows why concentrated, opaque control planes create systemic risk—and what observable, delayed, policy-constrained control can change.
The splashy piece on Intel and AMD TEEs falling to cheap physical interposers isn’t a plot twist so much as the epilogue.
Airport outages and casino recovery plans reveal the same lesson: isolate critical systems, constrain trust, and design deployment and recovery before an incident.
MPC removes single-key risk, but offchain transaction builders and policy APIs can still tell distributed signers to authorize the wrong operation.
The latest npm compromise showed how a tiny change deep in a dependency supply chain can rewrite what users see, sign, and send.
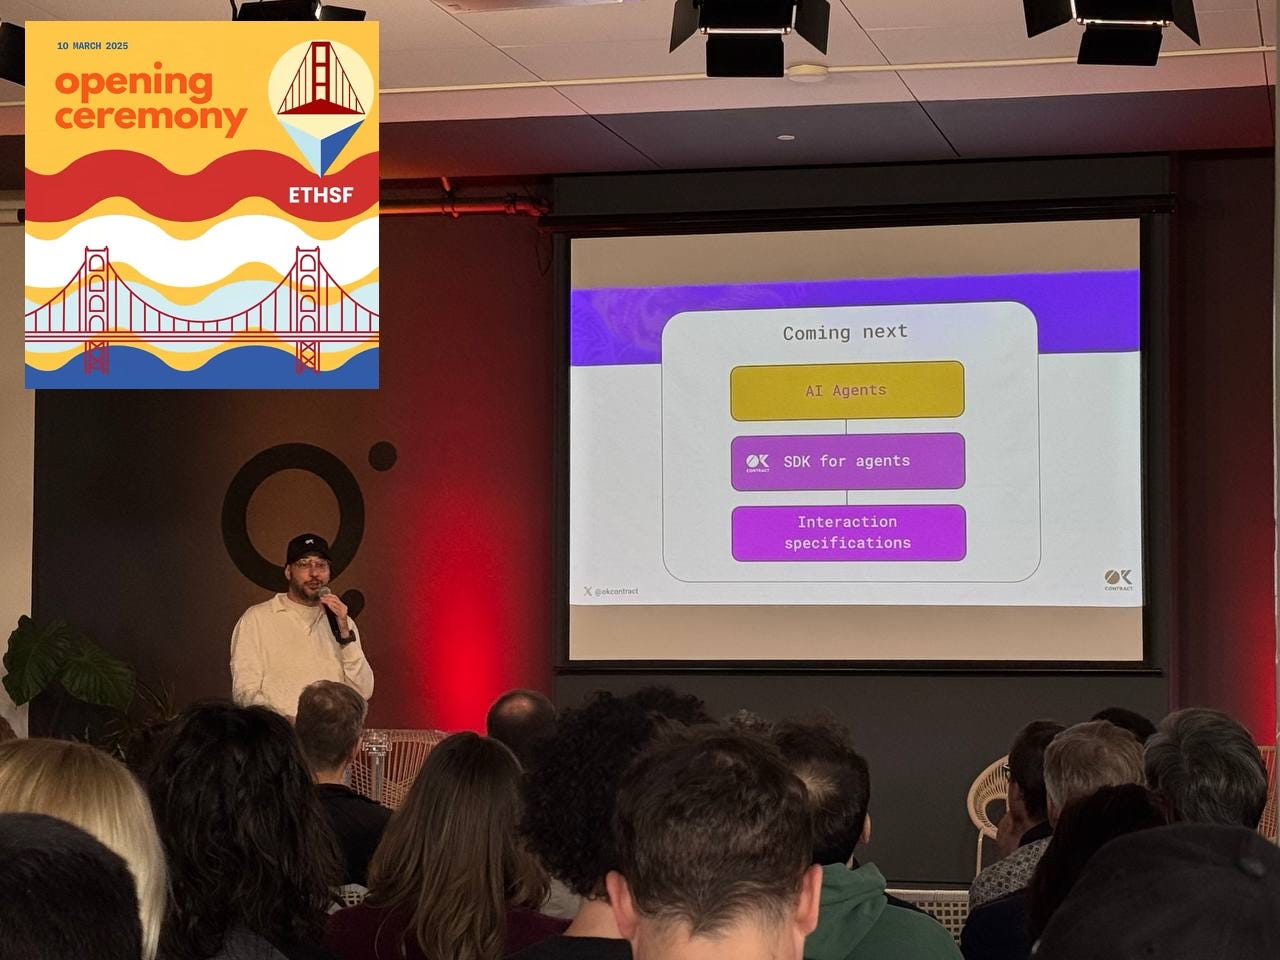
This year’s ETHSF brought together builders, researchers, and enthusiasts for a series of events covering both blockchain and AI developments.
What ETHDenver 2025 revealed about transactional AI agents, cross-chain liquidity, and the security infrastructure needed for both.
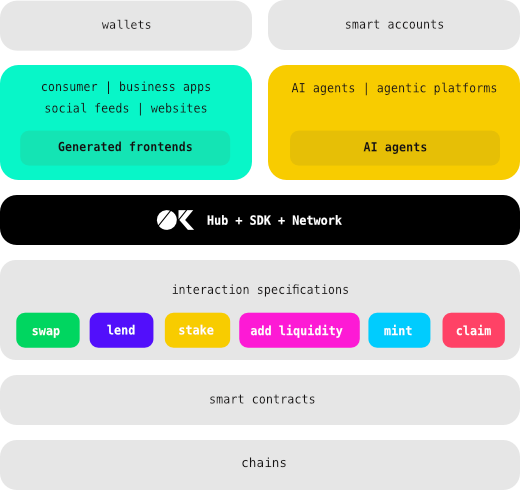
A practical architecture for connecting AI agents to smart contracts with constrained interactions, smart accounts, and verifiable transaction middleware.
ABI2UI is an open-source interface generator that turns smart-contract ABIs into usable forms, with readable parameters, integer conversion, and reusable constraints.
OKcontract 2.0 adds multi-account user IDs, shareable pages, clearer ABI navigation, interface refinements, and a set of reliability fixes.
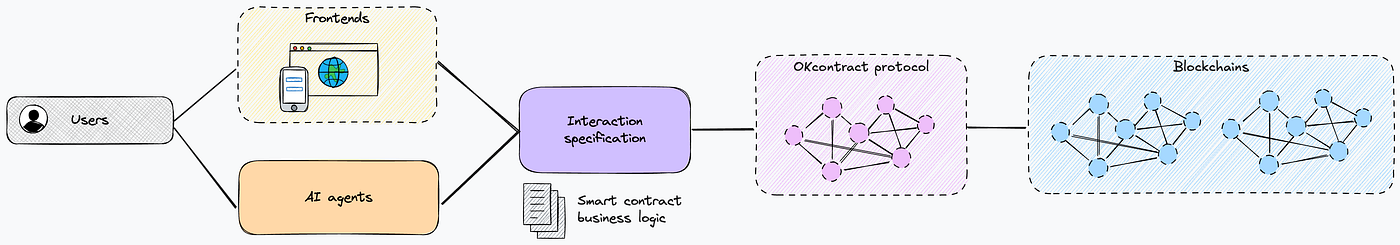
Why AI agents need deterministic, verifiable middleware before they can safely automate DeFi transactions and other onchain operations.
Fred is an open-source functional reactive editor for structured data, built on Cells as part of OKcontract's Optimism ABI2UI research grant.